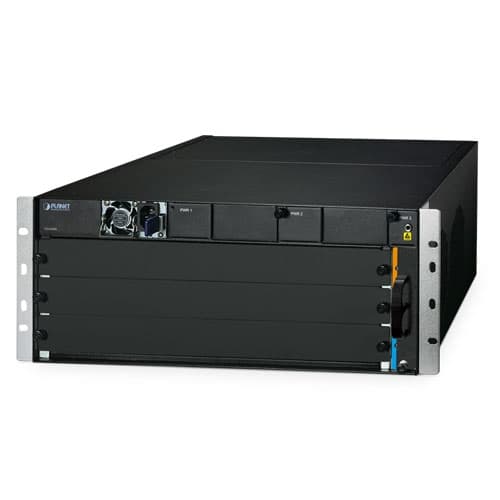
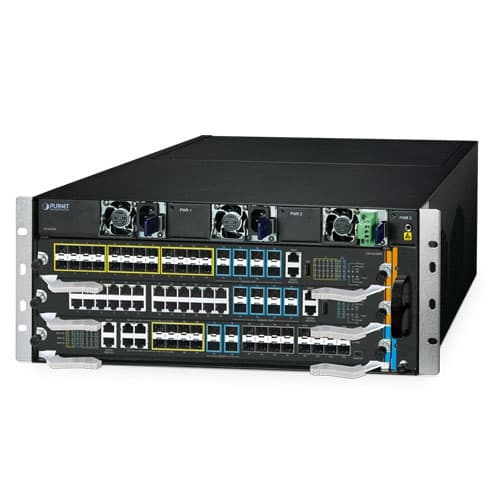
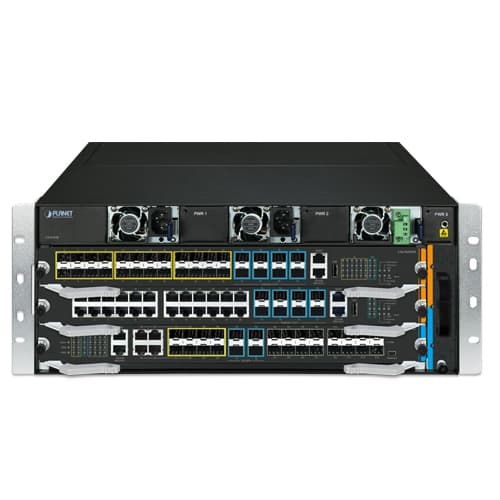
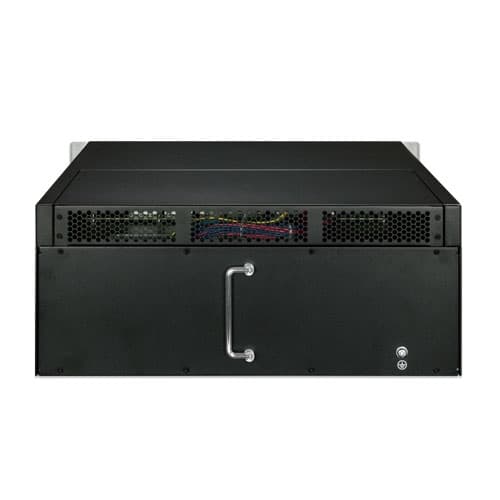
CS-6303R — 3-slot Layer 3 IPv6/IPv4 Routing Chassis Switch
3-slot Layer 3 IPv6/IPv4 Routing Chassis Switch
Confirma disponibilidad, instalación y entrega con un asesor.
Descripción
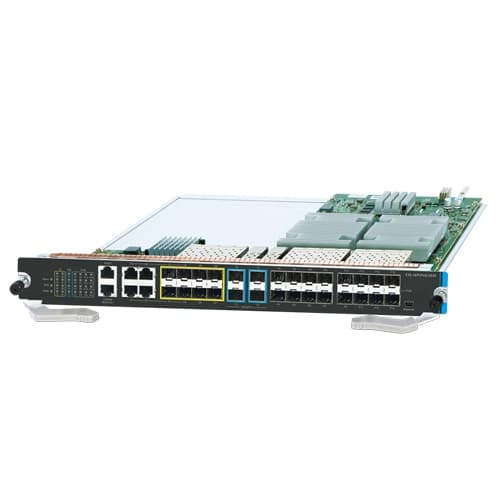
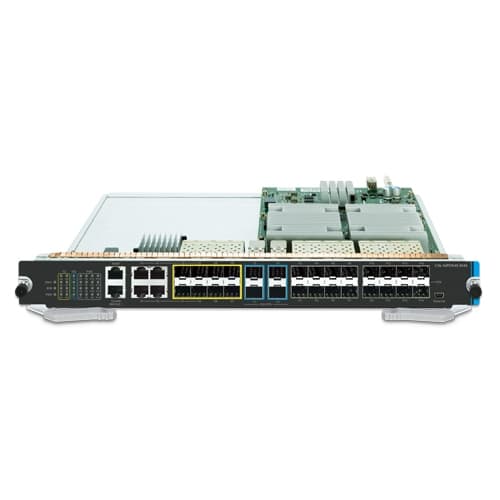
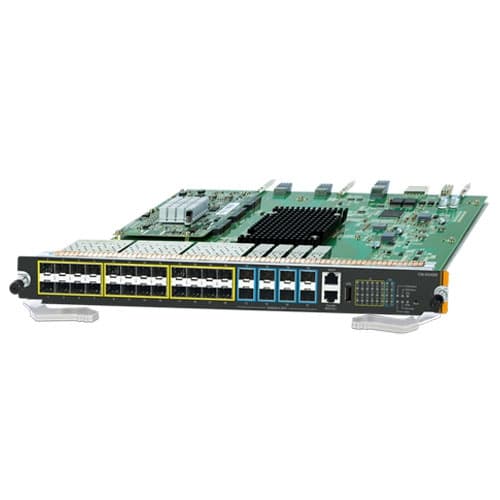
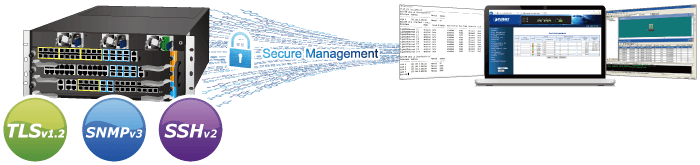
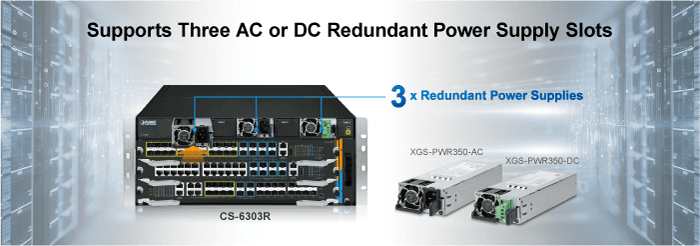
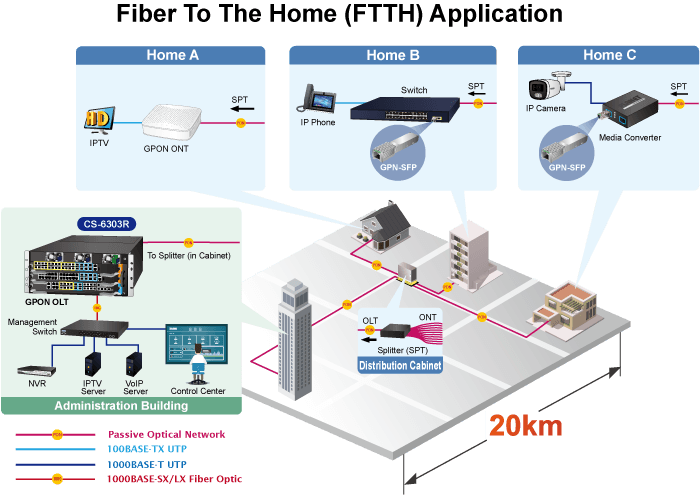
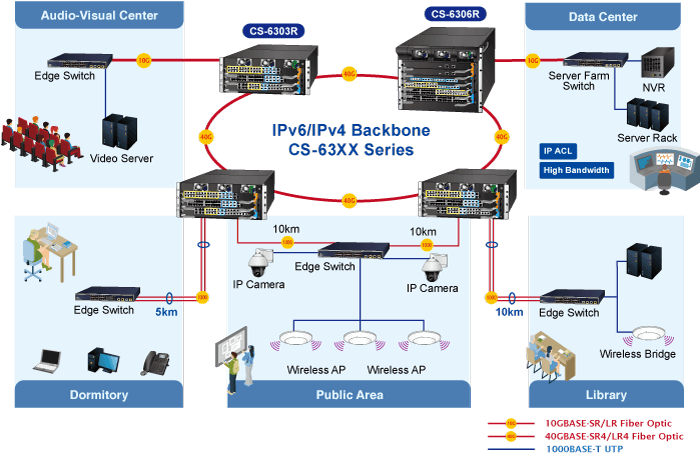
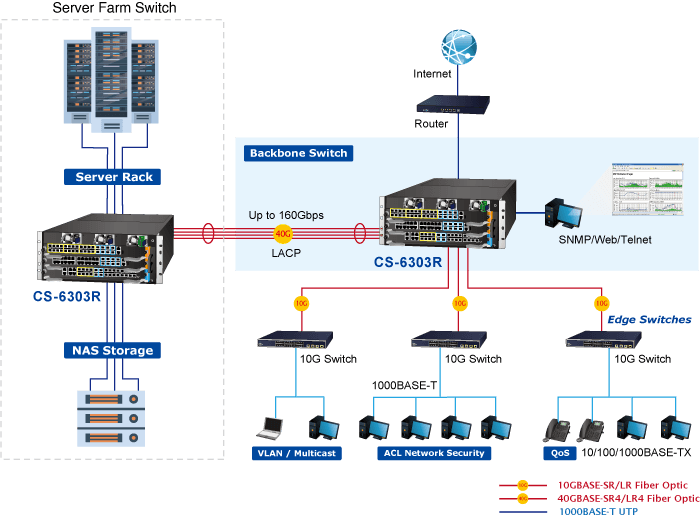
Outstanding Flexibility and High Performance PLANET CS-6303R Core Layer Routing Chassis Switch is specially designed for large network applications such as enterprises, campuses, communities, ISPs and data center networks where flexible configuration, large capacity, high density, high reliability and advanced traffic management are required. The CS-6303R is a high-density chassis switch built with three module slots and a redundant power supply. It provides great port flexibility for network deployment by offering various combinable management and switch modules. For instance, one management module can work with two switch modules, or two management modules can work together to perform system backup. The available modules for the CS-6303R chassis switch are listed below: Item CS-6303R Total Module Slots 3 Management Slots 2 (slots 2 and 3) Switch Slots 2 (slots 1 and 2) Power Supply Slots 3 Total Port Capacity Max. 10/100/1000BASE-T 120 Max. 1000BASE-X SFP Ports 120 Max. 10G SFP+ Ports 40 Max. 40G QSFP+ Ports 8 Max. GPON Ports 48 Positioned as the core layer switch, the CS-6303R serves ideally for large-sized networks and IP metropolitan networks by supplying advanced intelligent and secure features and giving high performance and flexibility. Scalable 10-Gigabit and 40-Gigabit Performance The CS-6303R chassis switch delivers Gigabit, 10-Gigabit and 40-Gigabit Ethernet connectivity in a highly-flexible and resilient modular platform. With a high switching capacity, it supports wire-speed L2/L3 forwarding and high routing performance for IPv4 and IPv6 protocols. The scalable and flexible modular architecture supports up to 1.47Tbps forwarding performance in a single system. They are ideal for the core layer of campuses, enterprise networks and the aggregation layer of IP metropolitan networks, and wide area networks. Rich Multi-Layer Networking Protocols The CS-6303R comes with the complete Layer 3 managed function with comprehensive protocols and applications to facilitate the rapid service deployment and management for both the traditional L2 and L3 networks. It supports advanced routing protocols, including RIP , RIPng , OSPFv2 and OSPFv3 . Strong Multicast The CS-6303R supports abundant multicast features. In Layer 2, it features IPv4 IGMPv1/v2/v3 snooping and IPv6 MLD v1/v2 snooping. With Multicast VLAN Register (MVR), multicast receiver/sender control and illegal multicast source detection functions can be had. In Layer 3, it features PIM-DM , PIM-SM and PIM-SSM which make it great for any robust networking. Full IPv6 Support The CS-6303R supports IPv4-to-IPv6 technologies including IPv4 manual/automatic tunnel , IPv6-to-IPv4 tunnel , and Intra-Site Automatic Tunnel Addressing Protocol ( ISATAP ) tunnel. It comprehensively supports IPv6 Neighbor Discovery, DHCPv6, Path MTU Discovery, IPv6-based Telnet, SSH and ACL, meeting the need of IPv6 network device management and service control. High Reliability The key components of the CS-6303R are the management module, power system, fan system, and redundant power design. All system modules support hot-swapping and seamless switching without manual intervention. The CS-6303R supports In-Service Software Upgrade ( ISSU ) and Graceful Restart ( GR ) for OSPF and BGP routing protocols, ensuring non-stop user data forwarding during the system is upgraded. It also supports Bidirectional Forwarding Detection ( BFD ), enabling fault detection and service recovery within seconds by integrating with Layer 2 or Layer 3 protocol. Redundant Ring, Fast Recovery for Critical Network Applications The CS-6303R supports a redundancy protection mechanism and feature strong, rapid self-recovery capability to prevent interruptions and external intrusions. It incorporates Layer 3 Virtual Router Redundancy Protocol ( VRRP ) protocol and Layer 2 Spanning Tree Protocol IEEE 802.1s MSTP (Multiple Spanning Tree Protocol) technology into customer’s network to enhance system reliability and uptime. In a simple ring network, the recovery time could be less than 50ms to quickly bring the network back to normal operation. Centralized Hardware Stacking Management The CS-6303R can be used to build a virtually logical facility, providing enterprises, service providers, and telecoms with flexible control over port density, uplinks, and switch stack performance. The chassis switch can be connected in a ring for redundancy, ensuring data integrity even if one switch in the stack fails. You can even hot-swap switches without disrupting the network, greatly simplifying the process of upgrading the LAN to meet increasing bandwidth demands. Powerful Security from Layer 2 to Layer 4 The CS-6303R offers comprehensive Layer 2 to Layer 4 Access Control List (ACL) for enforcing security to the edge. It can be used to restrict network access by denying packets based on source and destination IP address, TCP/UDP ports or defined typical network applications. Their protection mechanism also comprises 802.1x port-based and MAC-based user and device authentication. The private VLAN function prevents communication between edge ports, ensuring user privacy. Advanced IP Network Protection The CS-6303R also provides DHCP Snooping , IP Source Guard , and Dynamic ARP Inspection functions to prevent IP snooping attacks and discard ARP packets with invalid MAC addresses. Network administrators can now construct highly-secure corporate networks with considerably less time and effort than before. Enhanced Quality of Service The CS-6303R fully supports the DiffServ module, allowing users to specify queue bandwidth on each port. WRR, SP, and SWRR scheduling are also provided. The chassis switch supports port security to enable trusted CoS, DSCP, IP precedence, and port priority. Users can modify packets' DSCP and CoS values so that traffic can be classified by port, VLAN, DSCP, IP precedence, and ACL table. Users can also modify packets' DSCP and IP precedence values to allocate different bandwidths for voice, data, and video, customizing different levels of service quality. Efficient and Secure Management For efficient management, the CS-6303R is equipped with console, Web and SNMP management interfaces. With the built-in Web-based management interface, the chassis switch offers an easy-to-use, platform-independent management and configuration facility. For text-based management, it can be accessed via Telnet and the console port. To reduce product learning time, the chassis switch offers Cisco-like command via Telnet or console port and customer doesn’t need to learn new command from these switches. For standard-based monitor and management software, it offers SNMPv3 connection which encrypts the packet content at each session for secure remote management. Moreover, the chassis switch offers secure remote management by supporting SSHv2, TLSv1.2 and SSLv3 connection which encrypts the packet content at each session. Extractive Power Supply Design for Enhanced Flexibility The CS-6303R is equipped with an extractable 100–240V AC power supply unit, making it easy for users to replace the power module. Additionally, the chassis switch reserves two extra backup power slots on the front panel, allowing users to install a second AC or DC power supply for redundancy. The AC and DC power options are interchangeable. The redundant power system is specifically designed to meet the demands of high-tech facilities requiring maximum power integrity. Scalable High-performance GPON for FTTx Applications PLANET CS6-16PON4C4S4X GPON Optical Line Terminal (OLT) module consists of 16 GPON ports, four Gigabit TP/SFP combo ports, four Gigabit SFP ports, four 10G SFP+ ports, and one management port. It complies with ITU-T G.984/G.988 and meets the technical requirements for GPON OLTs in network access. It is easy to install and maintain a GPON deployment with up to 1024 ONU and HGU devices, providing highly-effective GPON solutions and convenient management for fiber optic broadband networks. It offers a high bandwidth of up to 2.5Gbps downstream and 1.25Gbps upstream , long-distance coverage of up to 20km between equipment nodes, and flexibility for network deployment. This is a cost-effective access technology that provides a reliable and scalable network for triple-play service applications, such as HDTV, IPTV, voice-over-IP (VoIP), and multimedia. Applications Carrier-class Backbone Switch for Campuses and Communities Designed for large-scale network communications in enterprises, campuses, and communities, PLANET CS-6303R chassis switch is the ideal choice for an affordable and scalable network solution. It offers a high-capacity chassis platform with exceptional quality and reliability, supporting 10/100/1000BASE-T, 1000BASE-SX/LX, 10GBASE-SR/LR, and 40GBASE-SR4/LR4 scalable solutions that can be integrated seamlessly into any large networks. The chassis switch can provide up to 120 high-density Gigabit Ethernet ports, 120 SFP ports, 40 10G SFP+ ports, 8 40G QSFP+ ports, or 48 GPON OLT SFP ports, enabling remote uplink connectivity within a single system. It supports uplinks to the edge network through 1Gbps to 40Gbps optical transceiver modules. Additionally, the chassis switch offers a comprehensive set of modules for complex networks, giving network managers the flexibility to expand large-scale networks as needed. Reliable, High-performance, and High-density Enterprise Backbone Switch The 10/40-Gigabit Ethernet-supported equipment has become an essential component of enterprise and network infrastructures. The CS-6303R is a cost-effective, high-density, and high-bandwidth solution designed to meet modern market demands. Its dedicated chassis architecture allows all modules within the platform to function as a single, high-capacity switch, delivering multiple high-performance 10/40-Gigabit Ethernet connections for enterprise, campus, or telecom backbone networks. The redundant management modules and three power supplies provide the chassis switch with uninterrupted network service. Moreover, all modules are hot-swappable, allowing for expansion or replacement without disrupting system operation. The chassis switch is ideal as a server farm switch for connecting to servers and is perfectly suited for network environments that require continuous access to critical business applications. Key Features Hardware and Performance 3 open module slots: Up to 2 Management Modules (Slot 2 and Slot 3) Up to 2 Switch Modules (Slot 1 and Slot 2) Hot-swappable switching modules 1 RJ45 serial console interface on Management Module for switch basic management and setup MGMT port on Management Module for HTTP server access Redundant Power System 3 power slots 100~240V AC and 36-72V DC power redundancy Active-active redundant power failure protection Backup of catastrophic power failure on one supply IP Routing Features IPv4 Routing protocol supports RIP v1/v2, OSPFv2 and BGP4 IPv6 Routing protocol supports RIPng, OSPFv3 and BGP4+ Routing interface provides VLAN routing mode Policy-based Routing (PBR) for IPv4 VRRP protocol for redundant routing deployment Supports route redistribution Multicast Routing Features Supports Multicast Routing Protocols: PIM-DM (Protocol Independent Multicast - Dense Mode) PIM-SM (Protocol Independent Multicast - Sparse Mode) PIM-SSM (Protocol Independent Multicast - Source-Specific Multicast Mode) Supports IGMP v1/v2/v3 Layer 2 Features Supports VLAN IEEE 802.1Q tag-based VLAN Provider Bridging (VLAN Q-in-Q, IEEE 802.1ad) supported GVRP for dynamic VLAN management Private VLAN Supports Link Aggregation 802.3ad Link Aggregation Control Protocol (LACP) Cisco ether-channel (static trunk) Supports Spanning Tree Protocol STP, IEEE 802.1D (Classic Spanning Tree Protocol) RSTP, IEEE 802.1w (Rapid Spanning Tree Protocol) MSTP, IEEE 802.1s (Multiple Spanning Tree Protocol, spanning tree by VLAN) Port mirroring to monitor the incoming or outgoing traffic on a particular port (many to 1) Loop protection to avoid broadcast loops Link Layer Discovery Protocol (LLDP) Ethernet OAM 802.3ah/802.1ag/ITU-Y.1731 Quality of Service Ingress shaper and egress rate limit per port bandwidth control 8 priority queues on all switch ports IEEE 802.1p CoS/DSCP/Precedence VLAN ID Policy-based ingress and egress QoS Multicast Supports IPv4 IGMP snooping v1, v2 and v3 Supports IPv6 MLD snooping v1 and v2 Querier mode support MVR (Multicast VLAN Registration) Security Authentication IEEE 802.1x port-based network access authentication Built-in RADIUS client to cooperate with the RADIUS servers RADIUS/TACACS+ users access authentication Access Control List IP-based Access Control List (ACL) MAC-based Access Control List (ACL) Time-based ACL DHCP Snooping to filter distrusted DHCP messages Dynamic ARP Inspection discards ARP packets with invalid MAC address to IP address binding IP Source Guard prevents IP spoofing attacks Management IPv4 and IPv6 dual stack management Switch Management Interfaces Console and Telnet Command Line Interface HTTP web switch management SNMP v1 v2 v3 switch management SSHv2, SSLv3, TLSv1.2 and SNMP v3 secure access SNMP Management Four RMON groups (history, statistics, alarms, and events) SNMP trap for interface Link Up and Link Down notification Built-in Trivial File Transfer Protocol (TFTP) client BOOTP and DHCP for IP address assignment System Maintenance Firmware upload/download via HTTP Reset button for system reboot Dual images DHCP Functions: DHCP Relay DHCP Option 82 DHCP Server User Privilege levels control Network Time Protocol (NTP) and SNTP Network Diagnostic SFP-DDM (Digital Diagnostic Monitor) ICMP remote IP ping Syslog remote alarm System Log Stacking Management Virtualized multiple CS-6303R switch integrated into one logical device Single IP address stack management, supporting up to 2 hardware units stacked together Stacking architecture supports redundancy Ring mode
Especificaciones técnicas
- Total Number of Slots
- 3
- Max. Management Module
- 2 (slot 2 and 3) Supports dual master control redundancy and automatic recovery
- Max. Switch Module
- 2 (slot 1 and 2)
- Number of Power Supply Bays
- 3
- Number of Fan Trays
- 1, hot-pluggable (2 axial fans)
- Dimensions (W x D x H)
- 482.6 x 376.2 x 178.2 mm (with rack-mount kit) 4U high
- Weight
- 11kg (empty) 14.4kg (Chassis with 1 AC power module and 1 management module)
- Power Requirement
- AC: Input 100-240V~, 5A Max 50~60 Hz DC: Input 36-72V , 12.7A Max
- Power Consumption
- <350W
- Module Name
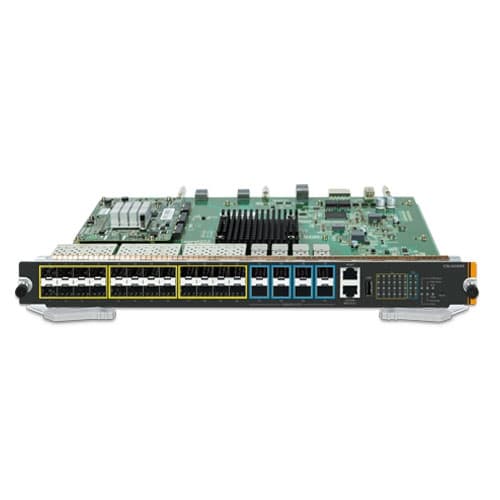
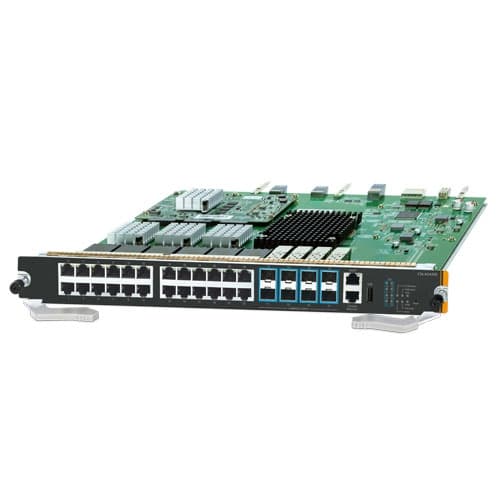
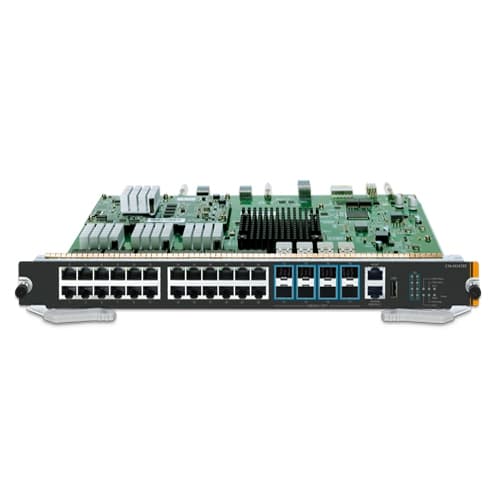
- CS6-M24S8X CS6-M24T8X
- CS6-M24S8X
- CS6-M24T8X
- Management Port
- One 10/100/1000BASE-TX RJ45 port
- Console
- One RJ45-to-RS232 serial port (9600, 8, N, 1)
- USB
- 1 x USB2.0 Type A for USB Storage device use
- Button
- Reset button: System reboot only
- 10/100/1000 RJ45 Ports
- - 24
- -
- 24
- 100/1000BASE-X SFP Ports
- 24 -
- 24
- -
- 10G SFP+ Ports
- 8 8
- 8
- 8
- CS6-S24S8X
- 24-Port 1000BASE-X SFP + 8-Port 10GBASE-X SFP+ Backward compatible with 100BASE-FX SFP transceivers
- CS6-S24T8X
- 24-Port 10/100/1000BASE-T + 8-Port 10GBASE-X SFP+ SFP+ slot is backward compatible with 1000BASE-X SFP transceivers
- CS6-S48T
- 48-Port 10/100/1000BASE-T
- CS6-S48S
- 48-Port 1000BASE-X SFP Backward compatible with 100BASE-FX SFP transceivers
- CS6-S24T24S
- 24-Port 10/100/1000BASE-T + 24-Port 1000BASE-X SFP
- CS6-S16X
- 16-Port 10GBASE-X SFP+ Backward compatible with 1000BASE-X SFP transceivers
- CS6-S4Q
- 4-Port 40GBASE-X QSFP+ Supports 40GBASE-SR4/LR4 QSFP+ transceivers and 40G QSFP+ to 4x10G SFP+ breakout cable
- CS6-16PON4C4S4X
- 16-Port xPON + 4-Port Gigabtit TP/SFP + 4-Port 1000BASE-X SFP + 4-Port 10GBASE-X SFP+ SFP+ slot is backward compatible with 1000BASE-X SFP transceivers
- Max. 10/100/1000BASE-T
- 120
- Max. 1000BASE-X SFP Ports
- 120
- Max. 10G SFP+ Ports
- 40
- Max. 40G QSFP+ Ports
- 8
- Max. GPON Ports
- 48
- Switch Processing Scheme
- Store-and-Forward
- Switch Throughput
- 552/1104 Mpps
- ACL Table
- Ingress Filter: 2816 Egress Filter: 512
- Routing Table
- IPv4 Protocol: 16K IPv6 Protocol: 16K
- MAC Address Table
- 32K
- ARP Table
- IPv4 16K \ IPv6 8K
- VLAN Table
- 4K VLAN entries
- Shared Data Buffer
- 32MB
- Multicast Table
- Layer3 2K Layer2 2K
- Flow Control
- IEEE 802.3x pause frame for full-duplex Back pressure for half-duplex
- Jumbo Frame
- 9216Bytes
- FLASH
- 64Mbytes
- RAM
- 1Gbytes
- IP Routing Protocol
- RIP v1/v2 OSPFv2 BGP (Border Gateway Protocol) Static routing
- Multicast Routing Protocol
- PIM-DM and PIM-SM PIM-SSM
- Routing Interface
- 256
- Routing Functions
- VRRP Policy routing Load balance through equal-cost routing GR (Graceful Restart) of OSPF and BGP BFD (Bidirectional Forwarding Detection) for OSPF and BGP IS-IS, Intermediate system to intermediate system
- IP Routing Protocol
- RIPng OSPFv3 BGP4+
- Routing Features
- Manual tunnel ISATAP tunnel 6-to-4 tunnel
- IPv6 Functions
- ICMPv6, DHCPv6, ACLv6, IPv6 Telnet IPv6 Neighbor Discovery Path MTU Discovery
- Port Configuration
- Port disable/enable Auto-negotiation 10/100/1000Mbps full and half duplex mode selection Flow control disable/enable Bandwidth control on each port Port loopback detect
- Port Mirroring
- TX/RX/Both Many to 1
- Link Aggregation
- Supports link aggregation cross switch module
- VLAN
- IEEE 802.1Q tag-based VLAN, IEEE 802.1ad Q-in-Q VLAN stacking/tunneling GVRP for VLAN management Private VLAN Up to 4K VLAN groups
- Spanning Tree Protocol
- IEEE 802.1D Spanning Tree Protocol (STP) IEEE 802.1w Rapid Spanning Tree Protocol (RSTP) IEEE 802.1s Multiple Spanning Tree Protocol (MSTP) BPDU protection, root protection
- IPv4 IGMP Snooping
- IPv4 IGMP v1/v2/v3 snooping IPv4 Querier mode support IGMP Filtering and IGMP Throttling IGMP Proxy reportin IGMP mmulticast forwarding Up to 8K multicast groups
- IPv6 MLD Snooping
- IPv6 MLD v1/v2 snooping Multicast VLAN Register (MVR) Up to 8K multicast groups
- QoS
- 8 priority queues on all switch ports Scheduling for priority queues Weighted Round Robin (WRR) Strict priority (SP) SP+WRR Traffic classification: IEEE 802.1p CoS DSCP DiffServ Precedence TOS VLAN ID IP ACL MAC ACL Policy-based ingress and egress QoS 802.1p and DSCP priority remark
- Storm Control
- Suppression of broadcast, multicast and unknown unicast packet
- Bandwidth Control
- Ingress and Egress At least 64Kbps stream
- Ring
- MSTP, IEEE 802.1s Multiple Spanning Tree Protocol
- Access Control List
- Supports Standard and Expanded ACL IP-based ACL MAC-based ACL Time-based ACL ACL based on: MAC Address IPv4/IPv6 IP Address Protocol-number sport/dport ToS/Precedence Ingress Filter: 2560 entries Egress Filter: 1024 entries
- Security
- MAC address limitation and MAC address filtering MAC sticky (IP + MAC + Port binding) Port isolation DHCP snooping, DHCP option 82 Dynamic ARP inspection IP source guard Defined against DoS or TCP attacks
- AAA
- TACACS+ and IPv4/IPv6 over RADIUS
- Network Access Control
- IEEE 802.1x port-based network access control
- System Configuration
- Console, Telnet and SSH Web browser SNMP v1/v2/v3
- Secure Management Interfaces
- SSHv2, SSLv3 Maximum 8 sessions for SSH and Telnet connection
- Management Interface
- CLI/MGMT/Telnet/SSH
- System Management
- IPv4 and IPv6 dual stack management SNMP MIB and TRAP SNMP RMON 1, 2, 3, 9 four groups Firmware upgrade by TFTP protocol through Ethernet network Configuration upload/download through TFTP protocol Supports IEEE 802.1ab LLDP protocol NTP and SNTP client RADIUS authentication for IPv4/IPv6 login user name and password Statistics analysis of sFlow and Netflow
- Event Management
- Remote syslog System log
- SNMP MIBs
- RFC 1213 MIB-II RFC 1215 Internet Engineering Task Force RFC 1271 RMON RFC 1354 IP-Forwarding MIB RFC 1493 Bridge MIB RFC 1643 Ether-like MIB RFC 1907 SNMPv2 RFC 2011 IP/ICMP MIB RFC 2012 TCP MIB RFC 2013 UDP MIB RFC 2096 IP forward MIB RFC 2233 if MIB RFC 2452 TCP6 MIB RFC 2454 UDP6 MIB RFC 2465 IPv6 MIB RFC 2466 ICMP6 MIB RFC 2573 SNMPv3 notification RFC 2574 SNMPv3 VACM RFC 2674 Bridge MIB Extensions
- Regulatory Compliance
- FCC Part 15 Class A, CE
- Standards Compliance
- IEEE 802.3 10BASE-T IEEE 802.3u 100BASE-TX IEEE 802.3z 1000BASE-SX/LX IEEE 802.3ab Gigabit 1000T IEEE 802.3ae 10Gigabit Ethernet IEEE 802.3ba 40Gigabit Ethernet IEEE 802.3x Flow Control and Back Pressure IEEE 802.3ad Port Trunk with LACP IEEE 802.1d Spanning Tree protocol IEEE 802.1w Rapid Spanning Tree Protocol IEEE 802.1s Multiple Spanning Tree Protocol IEEE 802.1p Class of Service IEEE 802.1Q VLAN tagging IEEE 802.1ad Double VLAN tagging (Q-in-Q) IEEE 802.1x Port Authentication Network Control IEEE 802.1ab LLDP IEEE 802.3az Energy Efficient Ethernet RFC 768 UDP RFC 783 TFTP RFC 791 IP RFC 792 ICMP RFC 2068 HTTP RFC 1112 IGMP v1 RFC 2236 IGMP v2 RFC 3376 IGMP v3 RFC 2710 MLD v1 RFC 3810 MLD v2 RFC 2328 OSPF v2 RFC 1058 RIP v1 RFC 2453 RIP v2 RFC 2080 RIPng for IPv6 RFC 2740 OSPFv3 for IPv6
- Operating
- Temperature: 0 ~ 50 degrees C Relative Humidity: 10 ~ 90% (non-condensing)
- Storage
- Temperature: -10 ~ 70 degrees C Relative Humidity: 5 ~ 90% (non-condensing)