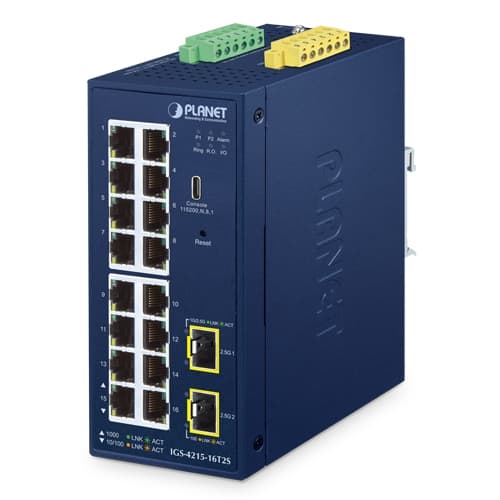
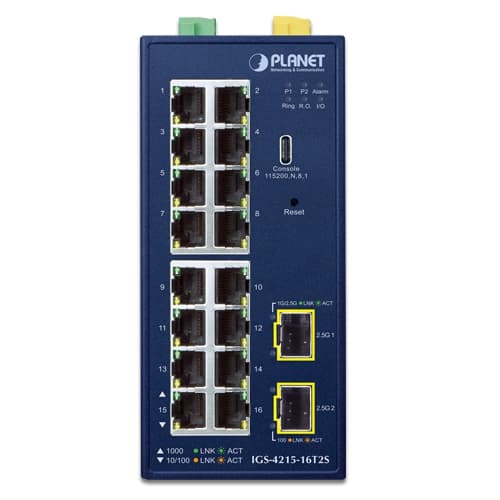
IGS-4215-16T2S — Industrial L2/L4 16-Port 10/100/1000T + 2-Port 1G/2.5G SFP Managed Switch
Industrial L2/L4 16-Port 10/100/1000T + 2-Port 1G/2.5G SFP Managed Switch
Confirma disponibilidad, instalación y entrega con un asesor.
Descripción
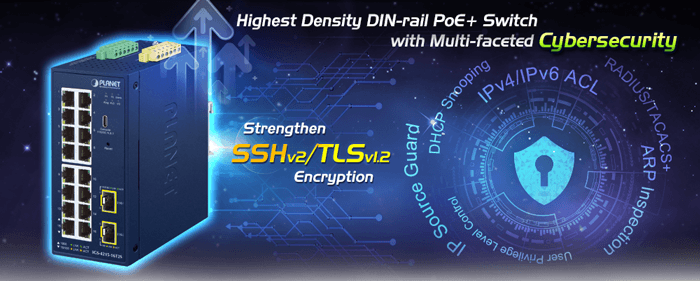
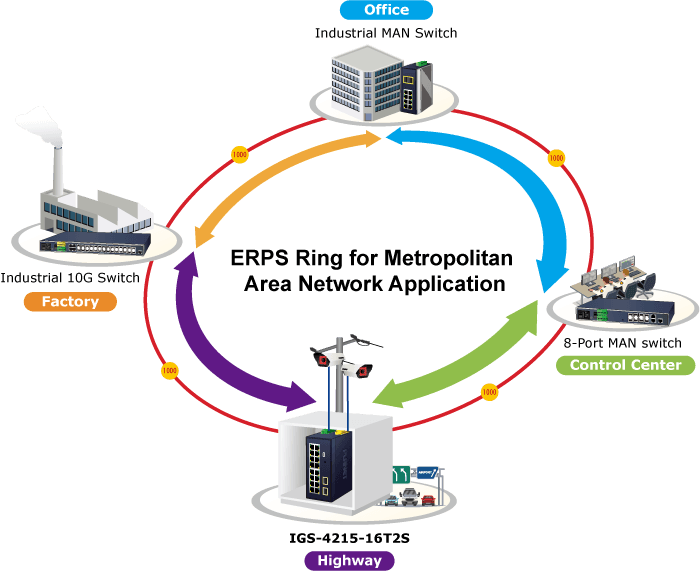
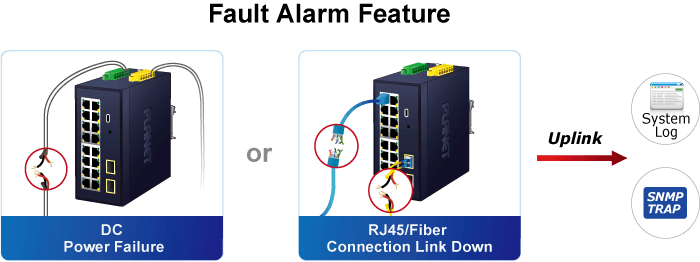
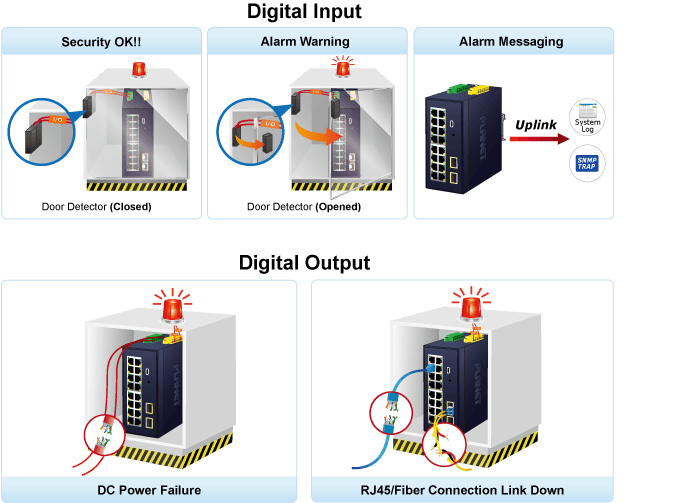
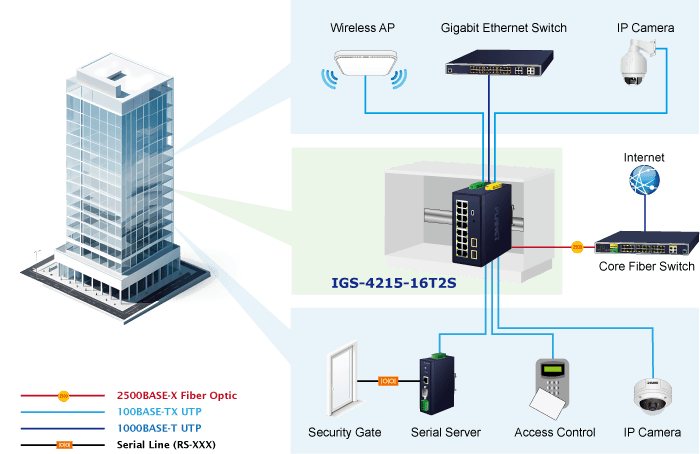
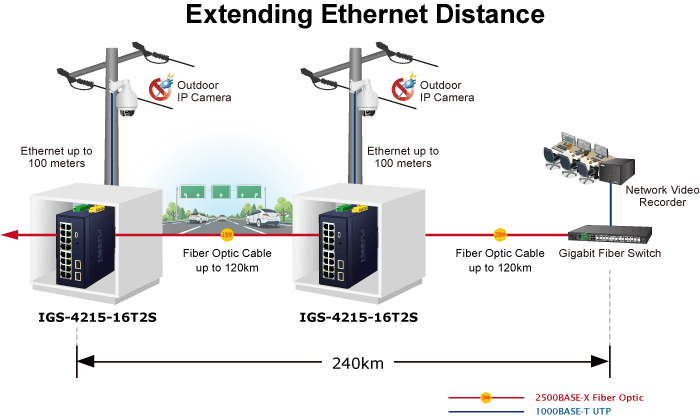
Cost-effective Full Solution Ideal for Hardened Environment Designed to be installed in heavy industrial demanding environments, the IGS-4215-16T2S is the new member of PLANET Industrial-grade, DIN-rail type L2/L4 Managed Gigabit Switch family to improve the availability of critical business applications. It provides IPv6/IPv4 dual stack management and built-in L2/L4 Gigabit switching engine along with 16 10/100/1000BASE-T ports, and 2 extra 100/1000/2500BASE-X SFP fiber slots for long-distance data and video uplink. The IGS-4215-16T2S is able to operate reliably, stably and quietly in any hardened environment without affecting its performance. It comes with operating temperature ranging from -40 to 75 degrees C in a rugged IP30 metal housing. Environmentally Hardened Design With the IP30 industrial case, the IGS-4215-16T2S provides a high level of immunity against electromagnetic interference and heavy electrical surges which are usually found on plant floors or in curb-side traffic control cabinets without air conditioner. Being able to operate under the temperature range from -40 to 75 degrees C, the IGS-4215-16T2S can be placed in almost any difficult environment. Cybersecurity Network Solution to Minimize Security Risks The IGS-4215-16T2S supports SSHv2 and TLSv1.3 protocols to provide strong protection against advanced threats. It includes a range of cybersecurity features such as DHCP Snooping, IP Source Guard, dynamic ARP Inspection Protection, 802.1x port-based network access control, RADIUS and TACACS+ user accounts management, SNMPv3 authentication, and so on to complement it as an all-security solution. Redundant Ring, Fast Recovery for Critical Network Applications The IGS-4215-16T2S supports redundant ring technology and features strong, rapid self-recovery capability to prevent interruptions and external intrusions. It incorporates advanced ITU-T G.8032 ERPS (Ethernet Ring Protection Switching) technology, Spanning Tree Protocol (802.1s MSTP) into customer’s network to enhance system reliability and uptime in various environments. Effective Alarm Alert for Better Protection The IGS-4215-16T2S supports a Fault Alarm feature which can alert the users when there is something wrong with the switches.With this ideal feature, the users would not have to waste time finding where the problem is. It will help to save time and human resource. Digital Input and Digital Output for External Alarm The IGS-4215-16T2S supports Digital Input and Digital Output on its front panel. This external alarm enables users to use Digital Input to detect and log external device status (such as door intrusion detector), and send event alarm to the administrators. The Digital Output could be used to alarm the administrators if the IGS-4215-16T2S port shows link down, link up or power failure. Robust Protection The IGS-4215-16T2S provides contact discharge of ±6KV DC and air discharge of ±8KV DC for Ethernet ESD protection. It also supports ±4KV surge immunity to improve product stability and protects users’ networks from devastating ESD attacks, making sure the flow of operation does not fluctuate. IPv6/IPv4 Dual Stack Management Supporting both IPv6 and IPv4 protocols, the IGS-4215-16T2S helps the SMBs to step in the IPv6 era with the lowest investment as its network facilities need not be replaced or overhauled if the IPv6 FTTx edge network is set up. Robust Layer 2 Features The IGS-4215-16T2S can be programmed for advanced switch management functions such as dynamic port link aggregation, 802.1Q VLAN, Q-in-Q VLAN, Multiple Spanning Tree Protocol (MSTP) , loop and BPDU guard , IGMP snooping , and MLD snooping . Via the link aggregation, the IGS-4215-16T2S allows the operation of a high-speed trunk to combine with multiple ports such as an 16Gbps fat pipe, and supports fail-over as well. Also, the Link Layer Discovery Protocol (LLDP) is the Layer 2 protocol included to help discover basic information about neighboring devices on the local broadcast domain. Efficient Traffic Control The IGS-4215-16T2S is loaded with robust QoS features and powerful traffic management to enhance services to business-class data, voice, and video solutions. The functionality includes broadcast/multicast/unicast storm control , per port bandwidth control , 802.1p/CoS/IP DSCP QoS priority and remarking. It guarantees the best performance in VoIP and video stream transmission, and empowers the enterprises to take full advantage of the limited network resources. Powerful Security PLANET IGS-4215-16T2S offers comprehensive IPv4/IPv6 Layer 2 to Layer 4 Access Control List (ACL) for enforcing security to the edge. It can be used to restrict network access by denying packets based on source and destination IP address, TCP/UDP ports or defined typical network applications. Its protection mechanism also comprises 802.1X port-based user and device authentication, which can be deployed with RADIUS to ensure the port level security and block illegal users. With the protected port function, communication between edge ports can be prevented to guarantee user privacy. Furthermore, Port security function allows to limit the number of network devices on a given port. The network administrators can now construct highly-secure corporate networks with considerably less time and effort than before. Advanced Network Security The IGS-4215-16T2S also provides DHCP Snooping , IP Source Guard and Dynamic ARP Inspection functions to prevent IP snooping from attack and discard ARP packets with invalid MAC address. The network administrators can now construct highly-secure corporate networks with considerably less time and effort than before. User-friendly and Secure Management For efficient management, the IGS-4215-16T2S is equipped with Command line, Web and SNMP management interfaces. With the built-in Web-based management interface, the IGS-4215-16T2S offers an easy-to-use, platform-independent management and configuration facility. For text-based management, it can be accessed via Telnet and the console port. By supporting the standard SNMP protocol, the switch can be managed via any SNMP-based management software. Moreover, the IGS-4215-16T2S offers secure remote management by supporting SSHv2 , TLSv1.3 and SNMP v3 connections which encrypt the packet content at each session. Flexible Long-distance Extension Solution The IGS-4215-16T2S provides 2 extra Gigabit TP interfaces supporting 10/100/1000BASE-T RJ45 copper to connect with surveillance network devices such as NVR, Video Streaming Server or NAS to facilitate surveillance management. Or through the two dual-speed fiber SFP slots , it can also connect with the 100BASE-FX /1000BASE-SX/LX SFP (Small Form-factor Pluggable) fiber transceiver to uplink to backbone switch and monitoring center in long distance. The distance can be extended from 550 meters to 2 kilometers (multi-mode fiber) and to 10/20/40/60/80/120 kilometers (single-mode fiber or WDM fiber). They are well suited for applications within the enterprise data centers and distributions. Intelligent SFP Diagnosis Mechanism The IGS-4215-16T2S supports SFP-DDM (Digital Diagnostic Monitor) function that can easily monitor real-time parameters of the SFP for the network administrator, such as optical output power, optical input power, temperature, laser bias current, and transceiver supply voltage. PLANET CloudNMS – Cloud-Based Universal Network Management PLANET’s CloudNMS platform and mobile app empower IT staff to remotely manage all network devices and Powered Devices (PDs) in real time. Designed for enterprises and industries, CloudNMS minimizes the need for on-site troubleshooting by providing centralized monitoring, fault detection, and instant alerts. With CloudNMS , businesses can manage diverse network deployments more efficiently, securely, and intelligently-all from a single cloud-based platform. Applications Industrial-grade Switch for Building Automation and Security Suitable for buildings where security is strictly to be enforced, the IGS-4215-16T2S, with sixteen high-speed Gigabit Ethernet interfaces, can easily build a power centrally controlled for an IP phone system, IP surveillance system, and wireless AP group in the harsh Industrial environment. Model that Withstands Harsh Operation and Extends Distance The IGS-4215-16T2S is made to withstand any harsh operation in such environments as traffic control cabinets, factory floors, and indoor and outdoor locations where temperatures are extremely high or low. With a non-blocking design and compact size, the installation of the IGS-4215-16T2S is easy and helpful to build a Gigabit high-bandwidth switched network quickly. Key Features Physical Port 16 10/100/1000BASE-T Gigabit Ethernet RJ45 ports 2 100/1000/2500BASE-X SFP slots for SFP type auto detection One USB Type C console interface for basic management and setup Industrial Case and Installation IP30 metal case DIN rail and wall-mount design 9~48V DC, redundant power with reverse polarity protection Supports 6000V DC Ethernet ESD protection -40 to 75 degrees C operating temperature Digital Input and Digital Output 2 digital input (DI) 2 digital output (DO) Integrate sensors into auto alarm system Transfer alarm to IP network via SNMP trap Switching Hardware-based 10/100Mbps (half/full duplex), 1000Mbps (full duplex), auto-negotiation and auto MDI/MDI-X IEEE 802.3x flow control for full duplex operation and back pressure for half duplex operation 8K MAC address table size 10K jumbo frame Automatic address learning and address aging Layer 2 Features Supports VLAN IEEE 802.1Q tagged VLAN Provider bridging (VLAN Q-in-Q, IEEE 802.1ad) support Protocol VLAN Voice VLAN Private VLAN (Protected port) Management VLAN GVRP Supports Spanning Tree Protocol STP (Spanning Tree Protocol) RSTP (Rapid Spanning Tree Protocol) MSTP (Multiple Spanning Tree Protocol) STP BPDU Guard, BPDU Filtering and BPDU Forwarding Supports Link Aggregation IEEE 802.3ad Link Aggregation Control Protocol (LACP) Cisco ether-channel (static trunk) Maximum 8 trunk groups, up to 8 ports per trunk group Provides port mirror (many-to-1) Loop protection to avoid broadcast loops Supports ERPS (Ethernet Ring Protection Switching) Link Layer Discovery Protocol (LLDP) Quality of Service Ingress/Egress Rate Limit per port bandwidth control Traffic classification IEEE 802.1p CoS TOS/DSCP/IP precedence of IPv4/IPv6 packets Strict priority and Weighted Round Robin (WRR) CoS policies Multicast Supports IPv4 IGMP snooping v2, v3 Supports IPv6 MLD snooping v1, v2 IGMP querier mode support IGMP snooping port filtering MLD snooping port filtering Security Storm Control support Broadcast/ unknown multicast/unknown unicast Authentication IEEE 802.1X port-based network access authentication Built-in RADIUS client to cooperate with the RADIUS servers DHCP Option 82 RADIUS/TACACS+ authentication Access Control List IPv4/IPv6 IP-based ACL IPv4/IPv6 IP-based ACE MAC-based ACL MAC-based ACE MAC Security Static MAC MAC filtering Port security for source MAC address entries filtering DHCP snooping to filter distrusted DHCP messages Dynamic ARP inspection discards ARP packets with invalid MAC address to IP address binding IP source guard prevents IP spoofing attacks DoS attack prevention Management IPv4 and IPv6 dual stack management Switch Management Interface Web switch management Console/Telnet Command Line Interface SNMP v1 and v2c switch management SSHv2, TLSv1.3 and SNMP v3 secure access SNMP Management SNMP trap for interface Link Up and Link Down notification Four RMON groups (history, statistics, alarms and events) User privilege levels control Built-in Trivial File Transfer Protocol (TFTP) client Static and DHCP for IP address assignment System Maintenance Firmware upload/download via HTTP/TFTP Configuration upload/download through HTTP/TFTP Dual images Hardware reset button for system reboot or reset to factory default SNTP Network Time Protocol Network Diagnostic Cable diagnostics ICMPv6/ICMPv4 Remote Ping SFP-DDM (Digital Diagnostic Monitor) Link Layer Discovery Protocol (LLDP) Protocol and LLDP-MED Event message logging to remote syslog server PLANET Smart Discovery Utility for deployment management PLANET NMS system and CloudNMS for deployment management
Especificaciones técnicas
- Copper Ports
- 16 10/100/1000BASE-T RJ45 auto-MDI/MDI-X ports
- SFP Slots
- 2 1000/2500BASE-SX/LX/BX SFP interfaces (Ports 17 to 18) Backward compatible with 100BASE-FX SFP
- Console
- 1 x USB Type C to RS232 serial port (115200,8, N, 1)
- Reset Button
- < 5 sec: System reboot > 5 sec: Factory default
- Connector
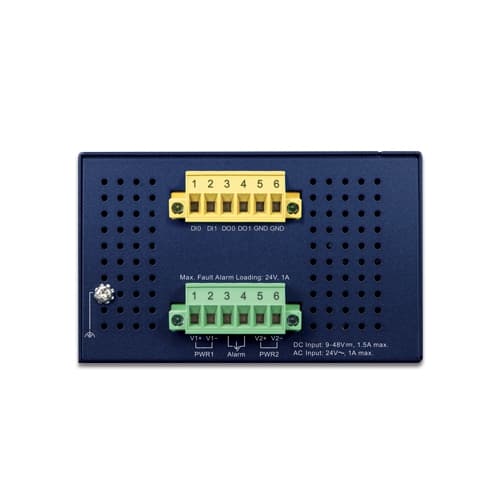
- Removable 6-pin terminal block Pin 1/2 for Power 1; Pin 3/4 for fault alarm; Pin 5/6 for Power 2 Removable 6-pin terminal block for DI/DO interface Pin 1/2 for DI 1 & 2, Pin 3/4 for DO 1 & 2, Pin 5/6 for GND
- Alarm
- One relay output for power failure. Alarm relay current carry ability: 1A @ 24V AC
- Digital Input
- 2 digital input (DI) Level 0: -24V~2.1V (±0.1V) Level 1: 2.1V~24V (±0.1V) Input load to 24V DC, 10mA max.
- Digital Output
- 2 digital output (DO) Open collector to 24V DC, 100mA max.
- Power Requirements
- Dual 9~48V DC 24V AC 50/60Hz
- Power Consumption
- Max. 3.31 watts/11.3BTU (System on) Max.10.41 watts/35.5BTU (Full loading)
- Dimensions (W x D x H)
- 66 x 107 x 152 mm
- Weight
- 829g
- Enclosure
- IP30 metal case
- Installation
- DIN-rail kit and wall-mount ear
- ESD Protection
- 6KV DC
- LED
- System: Power 1 ( Green ) Power 2 ( Green ) Alarm ( Red ) Ring ( Green ) R.O. ( Green ) I/O ( Red ) LNK/ACT ( Green ) Per 10/100/1000T RJ45Ports: 1000 LNK/ACT ( Green ) 10/100 LNK/ACT ( Amber ) Per SFP Interface: 1000/2500 LNK/ACT ( Green ) 100 LNK/ACT ( Amber )
- Switch Architecture
- Store-and-Forward
- Switch Fabric
- 42Gbps (non-blocking)
- Switch Throughput@64 bytes
- 31.25Mpps@ 64 bytes
- MAC Address Table
- 16K entries
- Shared Data Buffer
- 4Mbits
- Flow Control
- IEEE 802.3x pause frame for full duplex Back pressure for half duplex
- Jumbo Frame
- 12 Kbytes
- Port Mirroring
- TX/RX/Both Many-to-1 monitor Up to 4 sessions
- VLAN
- 802.1Q tagged VLAN 802.1ad Q-in-Q tunneling (VLAN stacking) Voice VLAN Protocol VLAN Private VLAN (Protected port) GVRP Management VLAN Up to 256 VLAN groups, out of 4094 VLAN IDs
- Link Aggregation
- IEEE 802.3ad LACP and static trunk Supports 8 groups with 8 ports per trunk
- Spanning Tree Protocol
- IEEE 802.1D Spanning Tree Protocol (STP) IEEE 802.1w Rapid Spanning Tree Protocol (RSTP) IEEE 802.1s Multiple Spanning Tree Protocol (MSTP) STP BPDU Guard, BPDU Filtering and BPDU Forwarding
- IGMP Snooping
- IPv4 IGMP snooping v2, v3 IGMP querier Up to 256 multicast groups
- MLD Snooping
- IPv6 MLD snooping v2, v3, up to 256 multicast groups
- QoS
- 8 mapping IDs to 8 level priority queues Port number 802.1p priority DSCP/IP precedence of IPv4/IPv6 packets Traffic classification based, strict priority and WRR Ingress/Egress Rate Limit per port bandwidth control
- Ring
- Supports ERPS, and complies with ITU-T G.8032 Recovery time < 450ms
- Access Control List
- IPv4/IPv6 IP-based ACL/MAC-based ACL IPv4/IPv6 IP-based ACE/MAC-based ACE Max. 256 ACL entries
- Port Security
- IEEE 802.1X – Port-based authentication Built-in RADIUS client to co-operate with RADIUS server RADIUS/TACACS+ user access authentication
- MAC Security
- IP-MAC port binding MAC filter Static MAC address, max. 256 static MAC entries
- Enhanced Security
- DHCP Snooping and DHCP Option82 STP BPDU guard, BPDU filtering and BPDU forwarding DoS attack prevention ARP inspection IP source guard
- Basic Management Interfaces
- RS232 to RJ45 Console Web browser Telnet SNMP v1, v2c
- Secure Management Interfaces
- SSHv2, TLSv1.3, SNMP v3
- System Management
- Firmware upgrade by HTTP/TFTP protocol through Ethernet network Configuration upload/download through HTTP/TFTP LLDP protocol SNTP PLANET Smart Discovery Utility PLANET NMS System/CloudNMS
- Event Management
- Remote/Local Syslog System log
- SNMP MIBs
- RFC 1213 MIB-II RFC 1215 Generic Traps RFC 1493 Bridge MIB RFC 2674 Bridge MIB Extensions RFC 2737 Entity MIB (Version 2) RFC 2819 RMON (1, 2, 3, 9) RFC 2863 Interface Group MIB RFC 3635 Ethernet-like MIB LLDP MIB PLANET-Aggr-MIB PLANET-DDMI-MIB PLANET-Firmware-MIB PLANET-GVRP-MIB PLANET-LACP-MIB PLANET-SYSUTIL-MIB
- Regulatory Compliance
- FCC Part 15 Class A, CE
- Stability Testing
- IEC 60068-2-32 (free fall) IEC 60068-2-27 (shock) IEC 60068-2-6 (vibration)
- Standards Compliance
- IEEE 802.3 10BASE-T IEEE 802.3u 100BASE-TX/100BASE-FX IEEE 802.3z Gigabit SX/LX IEEE 802.3ab Gigabit 1000BASE-T IEEE 802.3x Flow Control and Back Pressure IEEE 802.3ad Port Trunk with LACP IEEE 802.1D Spanning Tree Protocol IEEE 802.1w Rapid Spanning Tree Protocol IEEE 802.1s Multiple Spanning Tree Protocol IEEE 802.1p Class of Service IEEE 802.1Q VLAN Tagging IEEE 802.1x Port Authentication Network Control IEEE 802.1ab LLDP IEEE 802.3az for Energy-Efficient Ethernet RFC 768 UDP RFC 783 TFTP RFC 791 IP RFC 792 ICMP RFC 2068 HTTP RFC 1112 IGMP v1 RFC 2236 IGMP v2 RFC 3376 IGMP v3 RFC 2710 MLD v1 RFC 3810 MLD v2
- Operating Temperature
- -40 ~ 75 degrees C
- Storage Temperature
- -40 ~ 85 degrees C
- Humidity
- 5 ~ 95% (non-condensing)